
What happened
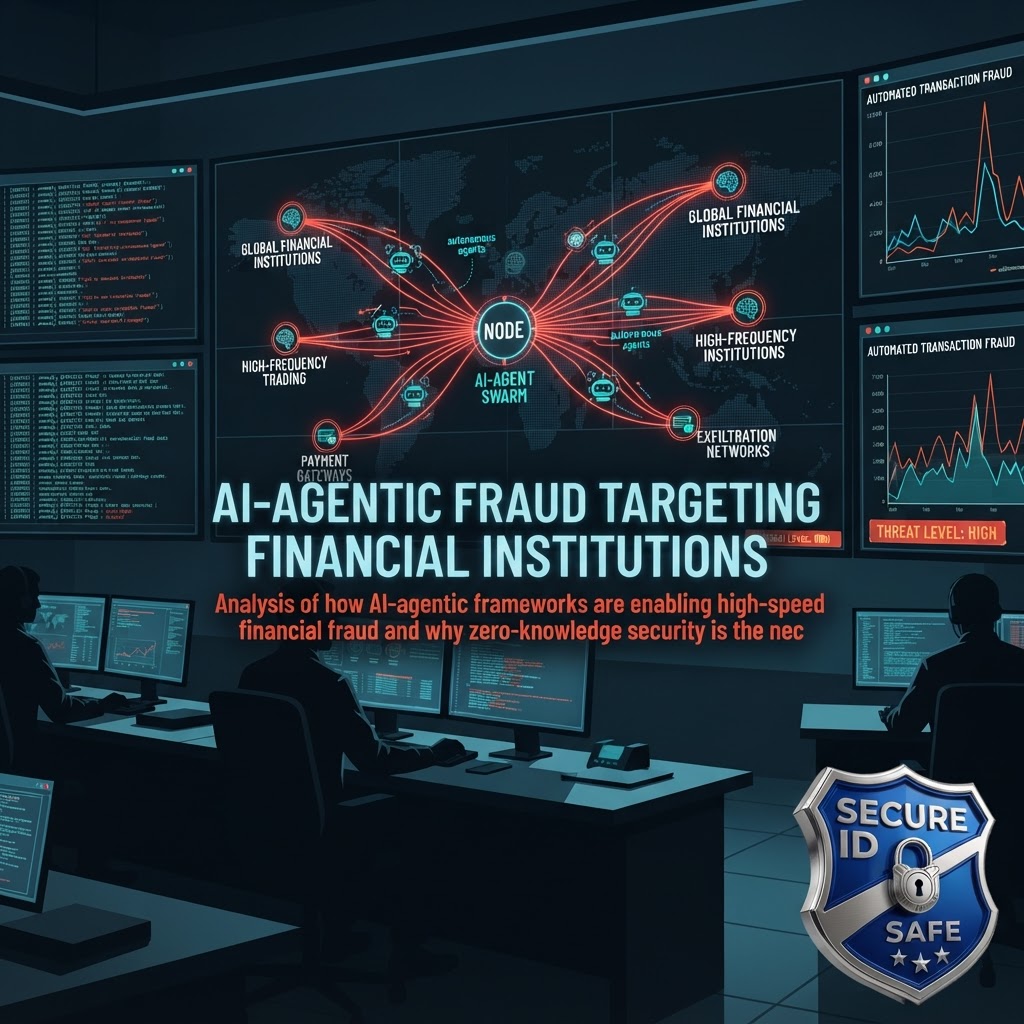
The Indian Cyber Crime Coordination Centre (I4C) and CERT-In have issued a critical warning regarding a new wave of cyberattacks targeting banks, NBFCs, and fintech firms. Attackers are utilizing 'Agentic AI Frameworks' to exploit unpatched software and misconfigured internet-facing servers. These AI agents operate at machine speed, allowing criminals to automate the compromise of financial systems, execute unauthorized fund disbursements via payment APIs, and rapidly route stolen capital through a network of 'mule' accounts to evade detection.
Why this matters
Traditional security perimeters are failing against the speed and adaptability of agentic AI. Because these attacks can autonomously navigate internal networks and adapt to security controls in real-time, the window for human intervention is effectively closed. This shift represents a move from manual, human-led hacking to automated, high-velocity theft that can drain institutional accounts before security teams even identify the initial breach.
How zero-knowledge changes this
In an environment where AI agents can compromise servers and exfiltrate data, zero-knowledge architecture provides a critical layer of defense. By utilizing client-side encryption, all sensitive data—including credentials, API keys, and financial records—is encrypted on the user's device before it ever touches a server. Because the provider never holds the encryption keys, even if an attacker successfully breaches a server or poisons an update system, they would only ever access useless ciphertext. Furthermore, robust seed recovery ensures that even if an attacker gains administrative access to a network, they cannot force a password reset or bypass authentication to access the underlying data, as the keys are derived locally from the user's device, not stored in a central database vulnerable to AI-assisted credential harvesting.