
What happened
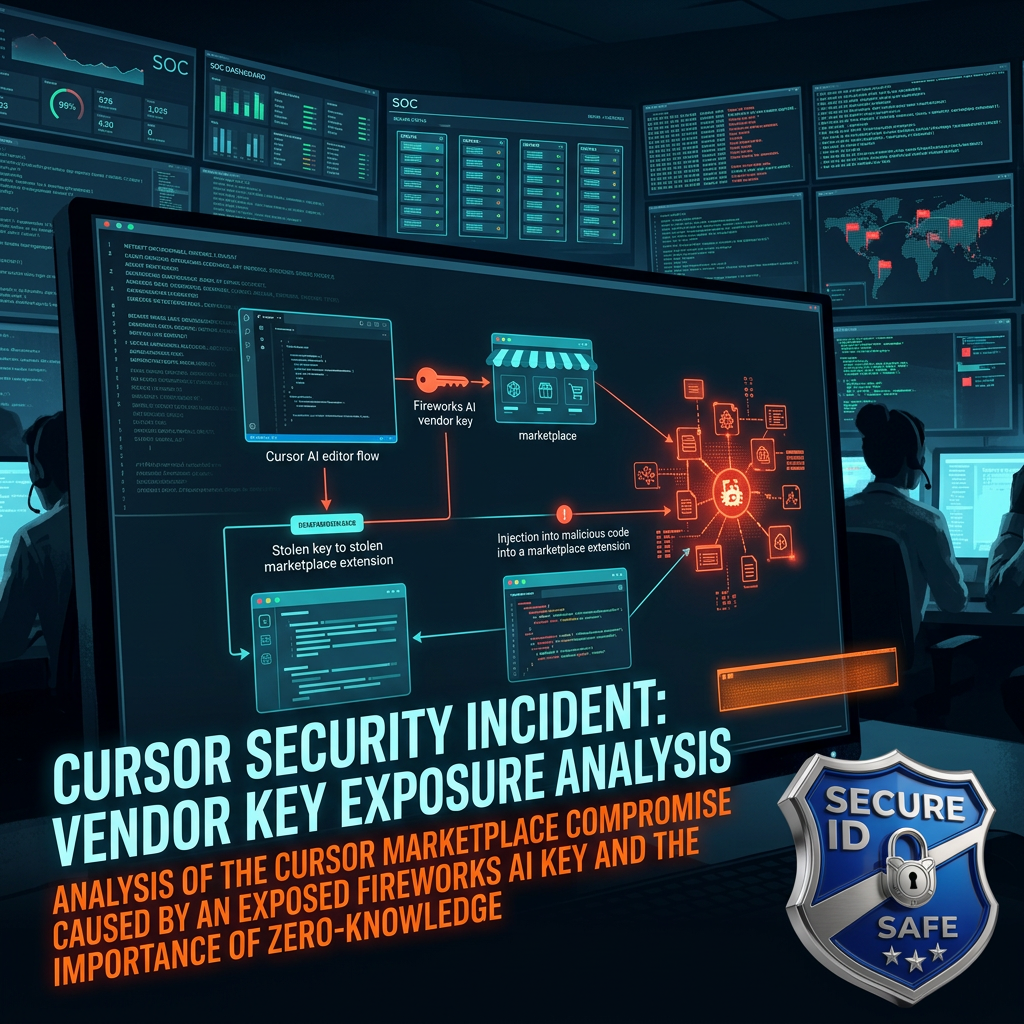
On October 29, 2026, AI code editor Cursor identified a security incident where an attacker used an access key stolen from third-party vendor Fireworks AI to infiltrate its systems. The attacker accessed historical coding agent traces containing unredacted credentials, which allowed them to pivot into internal SaaS tools and publish malicious versions of the Anthropic Claude Code extension (2.1.312 and 2.1.313) to the Cursor marketplace. The incident was contained by November 1, 2026.
Why this matters
This incident demonstrates how a single point of failure at a third-party vendor can lead to a supply-chain compromise of a widely used development tool. By harvesting unredacted credentials from logs, attackers gained the ability to distribute malicious code directly to developers, potentially compromising local environments and source code repositories.
How zero-knowledge changes this
SecureIDsafe's architecture would have neutralized this threat through its commitment to ciphertext-only storage and client-side encryption. In a zero-knowledge environment, even if an attacker gained access to a storage bucket or a vendor's infrastructure, they would only encounter encrypted blobs. Because SecureIDsafe uses device-derived keys that the provider never holds, the credentials stored within the platform would remain indecipherable to the attacker. Furthermore, our non-bypassable 24-word BIP-39 seed recovery ensures that even if an internal system were compromised, the master keys required to decrypt user data are never exposed in logs or traces, preventing the lateral movement seen in the Cursor incident.