
What happened
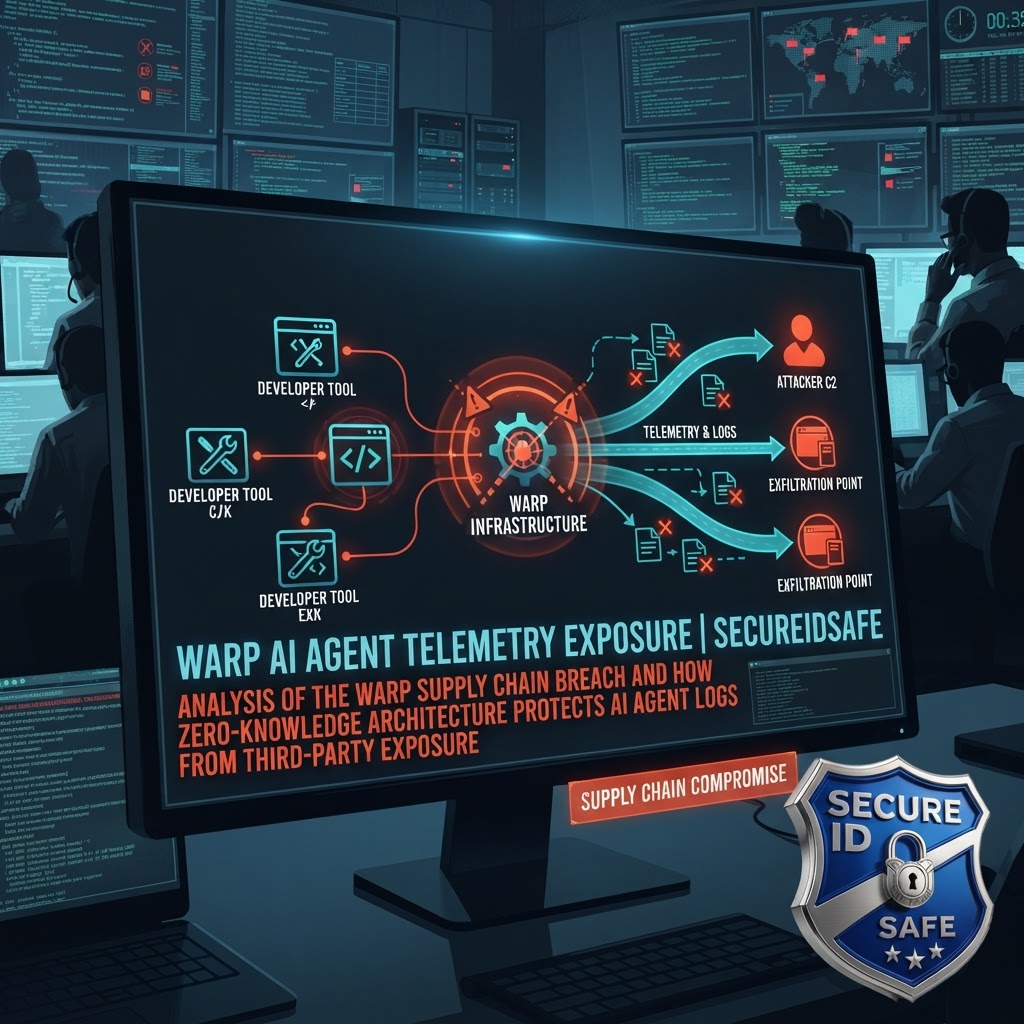
Developer-tool provider Warp disclosed on October 27, 2026, that attackers successfully exploited a third-party supplier within their infrastructure. This breach, detected on October 23, resulted in the unauthorized exposure of sensitive AI agent decision logs and telemetry data belonging to approximately 1% of their user base.
Why this matters
As organizations increasingly integrate AI agents into their development workflows, these agents often process proprietary code, internal logic, and sensitive operational data. When this data is stored in plain text or accessible via centralized cloud infrastructure, a single supply chain compromise can expose the entire "thought process" and decision-making history of an organization's AI, leading to potential intellectual property theft and further exploitation of internal systems.
How zero-knowledge changes this
SecureIDsafe’s architecture would have neutralized this exposure through client-side encryption. By utilizing AES-256 encryption with device-derived keys that the provider never holds, all telemetry and agent logs would be stored as ciphertext. Even if an attacker compromised the underlying infrastructure or a third-party supplier, they would only gain access to encrypted, indecipherable blobs. Because the decryption keys remain exclusively on the user's device and are protected by a non-bypassable 24-word BIP-39 seed recovery, the sensitive AI decision logs would remain private and inaccessible to unauthorized parties, ensuring that a breach of the storage layer does not equate to a breach of the data itself.